Veris
Fraud checks that cite their evidence, and a ledger that can't be quietly edited
- Status
- Hackathon prototype
- Year
- 2026
- Rooms
- ML & Impact, AI & Agents
Problem
Most scam detectors give a verdict without saying how they know, and incident reports are easy to alter after the fact.
Approach
Deterministic checks against named sources produce every verdict, each signal with its citation; a language model only explains the evidence in plain English or a regional language. Incidents go into a tamper-evident ledger and an NCRP-ready packet.
Engineering decisions
- The rules module is the only writer of a verdict; the explanation type has no verdict field.
- Never accuses definitively and never contacts an officer automatically — every portal link is user-tapped.
- Release build requests only network permissions.
What it does
- Share-sheet intake on Android
- Cited evidence panel
- Hash-chained incident ledger
- APK static analysis
Stack
My part
All 66 commits in the repository are mine.
Limits, stated plainly
- Prototype evaluated on its own adversarial demo set, not field data.
Evidence
- Veris README: status table and definition of done
- STATE.md
Verified demo output
$ python scripts/demo_all.py
homoglyph lookalike domain ........ caught, cited
Marathi explanation ............... generated (explains only)
fake-loan APK manifest ............ flagged
ledger tamper ..................... detected
adversarial set ................... Veris 9/9 · naive detector 5/9
91 tests + 4/4 demos pass on a clean machine, no keys
Screenshots
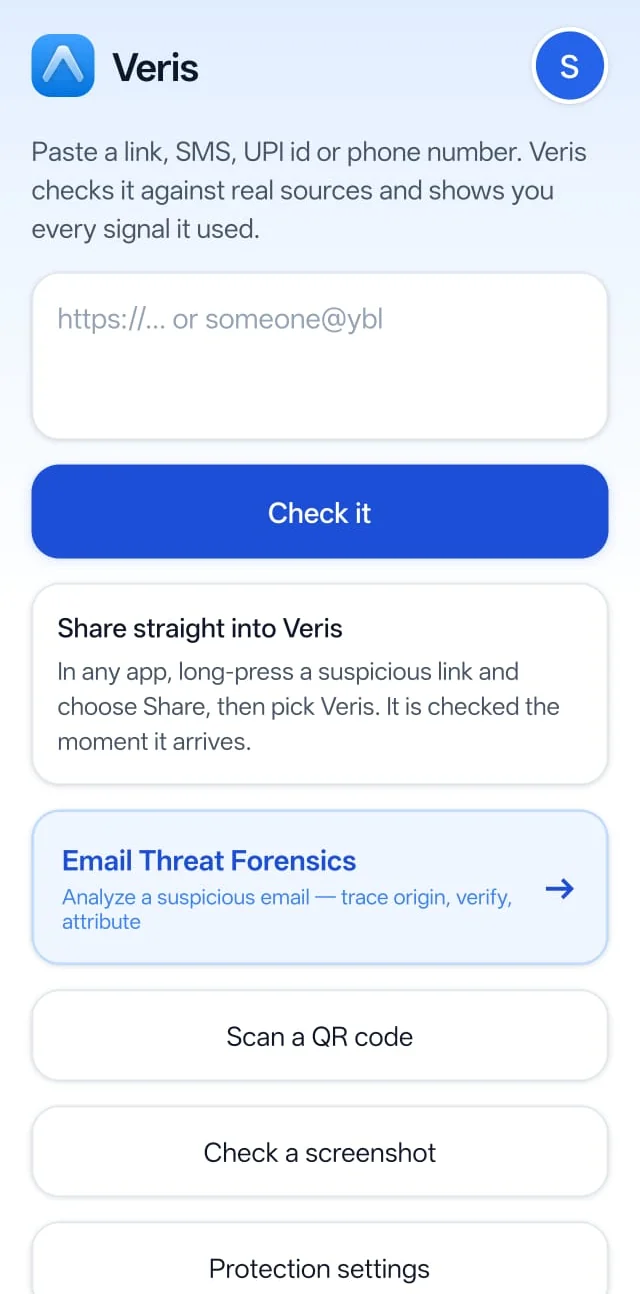
Veris home screen on Android: paste a link, SMS, UPI id or number to check it, with share-sheet, email forensics, QR and screenshot checks
Veris welcome screen: works offline, on-device